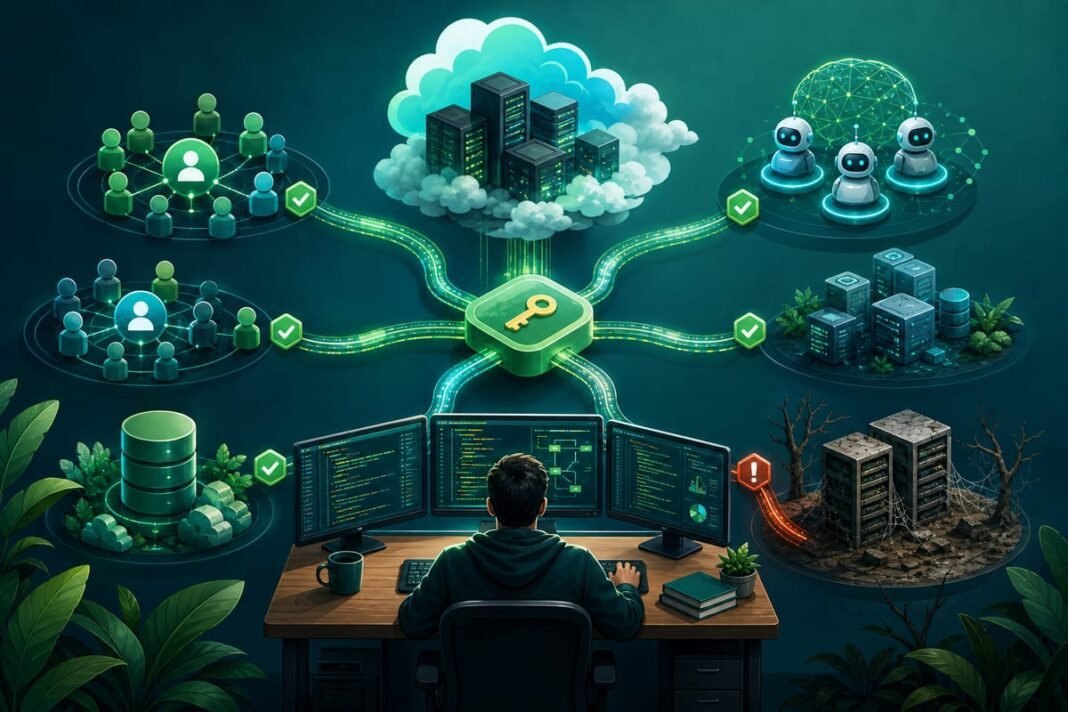
Unrecorded SaaS connections, forgotten API keys, or temporary development spaces can give AI agents access to all internal data. Few organizations would be aware of these accesses. The problem is not limited to tools used without authorization: initially approved rights may persist after a trial.
Tokens can survive deprivation
Revoking a compromised key or an integration deemed risky does not necessarily cut off all access paths. Other agents or integrations may cache their own tokens, including those used to refresh permissions. These elements can then automatically renew access in the background.
Identifiers and delegated authorizations concentrate most of the difficulties: OAuth consents, abandoned API keys or service accounts. Another mechanism, called “permission flattening”, concerns AI processing chains, notably retrieval augmented generation (RAG): they can ingest the data with a service account with extended rights.
Unintentional access would represent a greater risk than deliberate transmissions to unapproved tools. In many cases, an integration authorized for a brief experiment retains its rights once it is completed.
An employee can authorize a connection without control
A simple click on “Allow” can trigger unauthorized access to company information. When employees can provide consent themselves, a connection can be validated without going through purchasing or the IT team. The tools concerned may request extended rights to messaging, shared directories or customer relationship management software.
The evening letterFree · 7 p.m.
Do you code with AI?
Deciphered AI dev tools, agents and new features, every evening in 5 minutes. Free.
Included upon registration: our selection of the best AI guides & comparisons.
Choose your pace
Free · No spam · Unsubscribe in 1 click
Common uses include an agent programmed by a sales team to automatically update customer records in the organization. Agents linking multiple SaaS software are particularly difficult to detect and control, as their operation remains entirely in the background.
Testing can disperse internal data
On the development side, creating an API key to consult customer data and forgetting an environment used to test an agent are common situations. Abandoned development spaces constitute a persistent difficulty. Cloud-hosted platforms make it easy to copy to locations unknown to IT or security teams.
AI accentuates this difficulty: an API key can directly link a large third-party language model or agent to a data repository. Projects can also leave indexes, test sets, and logs outside of existing governance arrangements.
The majority of security professionals interviewed do not see this as a new problem. The cloud and SaaS software created comparable difficulties of dispersion and control two decades ago. It is the speed and extent of the phenomenon that have changed; The pace of AI development and deployment would exceed the tracking capabilities of most cybersecurity and data governance teams.