When you send a question to an AI service, you think you are speaking to a single person. The reality is more complex and more worrying. The researcher HD Mooredirector of research at the cybersecurity company Dragospublished on November 19, 2026 the results of a five-month experiment: he sent approximately two million prompts trapped to AI services and tracked what happened to the secrets they contained. He found traces of hacking at three model hostsresellers who exploit their customers’ requests, and privacy settings that don’t always protect.
An experience based on traps
From July to November 2026, the Dragos team inserted into each prompt unique and monitored items: real access keys to Amazon’s cloud, linked to empty and fully monitored accounts, passwords, web addresses and domain names. Each item was associated with a specific prompt, provider, intermediary, and privacy setting.
The team also developed techniques to trace the path of AI requests, similar to a network diagnostic tool. On approximately 2,000 paths analyzed, hundreds contained unidentified systemsthat is to say intermediaries of which the client was not aware.
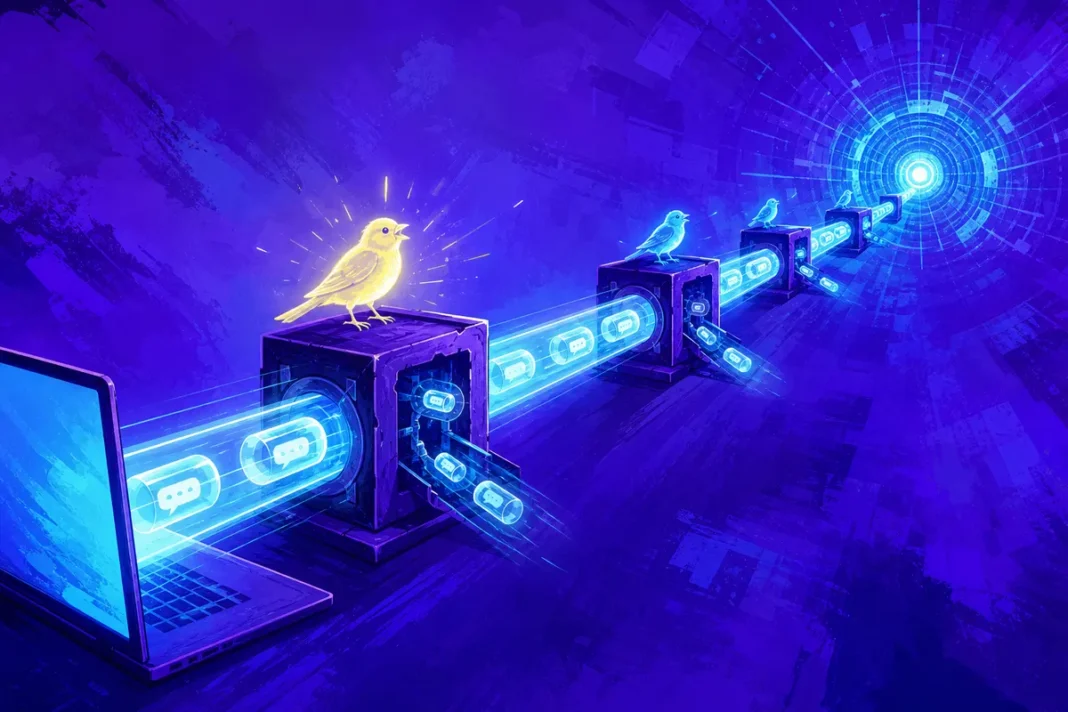
To understand the issue, you need to know how access to AI models works. The same model, especially if it is open weight, can be offered by many hosts different, which run it on their own servers. Of the routers offer a single point of access and redirect each request to one of these hosts, depending on price or availability. Of the marketplaces finally allow resellers to offer this access in turn.
This system has advantages: it allows you to compare offers, pay less and easily change models. But each additional link is one more organization that can see the content of the requests. A request can thus pass through several routers before reaching the server which actually runs the model, without the user being aware of it.
HD Moore is no stranger to the world of computer security: he is notably the creator of Metasploit, a penetration testing tool very popular among professionals.
Three hosts unknowingly hacked
The most serious discovery concerns three AI model hostsnot named. Attackers intercepted customer requests there. None of the three had noticed it before being warned by Dragos, and the oldest incident dates back to mid-July.
In the most important case, approximately 200 access keys booby traps were stolen during several short periods at the end of October. Some even came from requests rejected before reaching the modela sign that the attacker copied the data upon entering the service. The stolen keys were tested within hours: the attackers explored online storage, searched for secret vaults, attempted to activate hosted templates and create accounts to maintain access. Dragos recorded tens of thousands of calls made with his fake keys.
According to Cybersecurity Media, the team also observed the use ofARTEXthe AI-powered penetration testing tool recently linked to the attack on the European Commission, but only to check whether the stolen credentials still worked.
Resellers who use
The study highlights another weak link: marketplaces where resellers offer access to AI models, often at discounted prices. Some of them collected customer secrets without any software flawssimply by enabling query logging, a standard feature.
Dragos describes a pattern: sellers offer low-cost models, enable query recording, and wait. In one case, secret links sent through a seller were opened, followed by attempts to guess usernames. The same prompts sent to the same model by another seller have not been touched. In another case, a router discreetly transferred part of its traffic to this same marketplace, without informing its customers.
Privacy settings ignored
Final lesson: options supposed to protect data do not always keep their promises. Some requests stolen from hacked hosts were marked “Zero Data Retention”i.e. without data retention. This setting obviously offers no protection against an attacker already present in the infrastructure.
More disturbing, the systems of a Chinese AI laboratory unnamed have viewed the secret links of more than half prompts sent to its models between July and October, including around two thirds of requests marked without collection or retention. In one case, a link sent in a query without preservation appeared 24 days later in a Chinese company messaging service. The behavior was not unique to Chinese actors: a U.S. provider continued to view a secret link more than two months after a single request. Dragos could not determine whether these failures were intentional or due to bugs.
The study does not conclude that we must give up on AI, but that we must treat our suppliers with the same vigilance as any critical service provider. The recommendations that emerge:
- never keep secrets in a prompt: passwords, access keys, authentication tokens or confidential source code have nothing to do there;
- favor a direct relationship with established suppliers for sensitive data, rather than unknown resellers with attractive prices;
- with a router which distributes requests between several models, choose explicitly hosts rather than accepting the default selection;
- do not trust blindly non-custody options: they do not protect against a compromised intermediary;
- for the most sensitive data, considerhost a model on your own serversmore expensive but safest solution.
The risks linked to access keys are not new: developers have already paid the price when OpenCode was hacked, which increased their AI bills.
AI supply chain under scrutiny
This study highlights a blind spot in the adoption of AI in business: we rarely know who actually processes their data. Between the application used, the router, the reseller and the host of the model, a request can pass through several hands. For security managers, the question is no longer just whether a model is secure, but whether each organization that manipulates the data being sent can be identified. In Europe, the GDPR already requires companies to know their subcontractors: the Dragos study shows that, for AI, this requirement is far from simple to respect.