Linux runs most Internet servers, Android smartphones and many connected objects. THE November 4, 2026OpenAI announced that a chain of artificial intelligence agents discovered and exploited 948 distinct vulnerabilities of its core, the heart of the system. All allow an ordinary user to take full control of a machine. The cost of the operation, approximately $1.2 million, and its speed illustrate a change of scale in the search for vulnerabilities, with consequences for defenders and attackers alike.
Why the Linux kernel matters so much
THE core is the central part of an operating system: it manages memory, processors, files and communication with the hardware, and decides what each program is allowed to do. Linux is free software, developed for more than thirty years by thousands of contributors, and has tens of millions of lines of code.
It is found everywhere: in the vast majority of servers that run websites and online services, in cloud infrastructures, in Android smartphones, internet boxes, connected televisions or cars. Distributions, such as Debian, Ubuntu or Red Hat, integrate it with their own tools and distribute its updates. A flaw in the kernel can therefore affect a considerable number of devices, often without their users knowing it.
A nearly autonomous agent chain
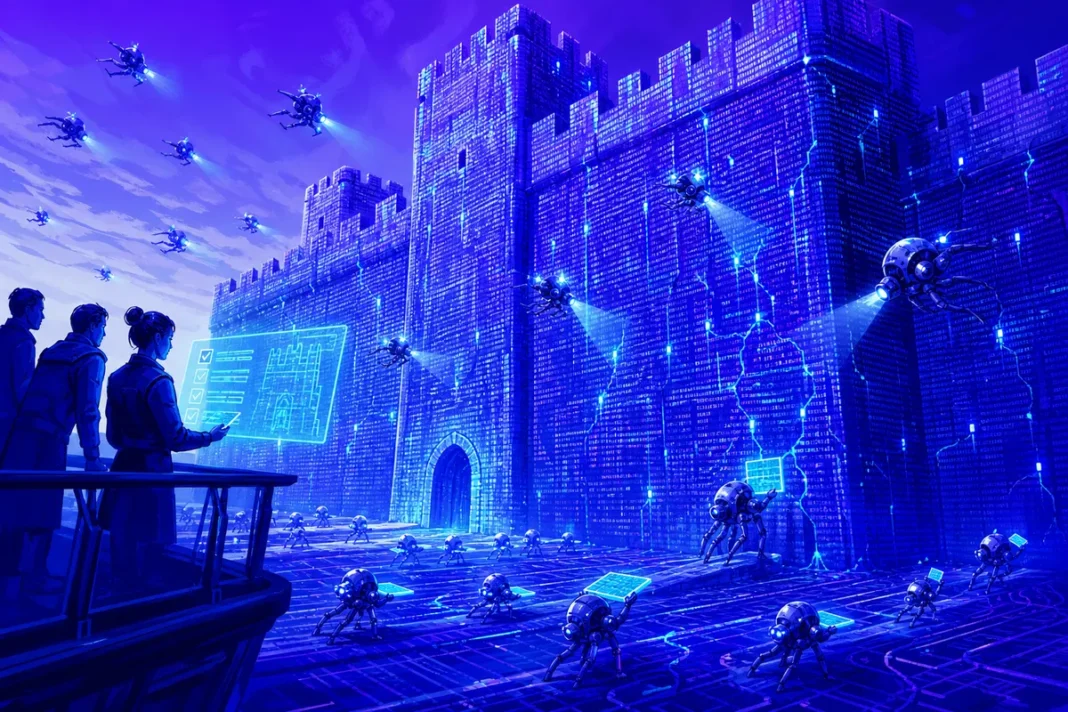
According to the OpenAI report, entitled “A thousand fewer paths to root”, the campaign took place mid-October 2026 with a future model specialized in cybersecurity, the name of which OpenAI has not revealed. The chain works in five stages: discovery of flaws, validation in real conditions, evaluation of their exploitability, writing of fixes and human proofreading.
Concretely, scout agents first targeted 5,034 areas of the code, or approximately 2.8 million lines. Analyst agents identified 2,308 potential vulnerabilities in twelve hours. Each was then replicated in isolated virtual machines, which confirmed 1,724 vulnerabilities in thirty hours. Finally, specialized agents wrote the attacks and proposed a fix for each flaw. OpenAI security researchers reviewed the results before transmitting them to the kernel maintainers.
| Stage | Result announced |
|---|---|
| Potential vulnerabilities identified | 2,308 |
| Reproduced vulnerabilities | 1,724 |
| Functional privilege escalation attacks | 1,169 |
| Corresponding distinct faults | 948 |
| Evidence of information leakage | 291 |
| Total cost in calculation | About $1.21 million |
| Cost per distinct flaw | About $1,280 |
A change of scale
The figure first impresses with its volume. According to Interesting Engineering, a previous campaign, conducted in July 2026 with the GPT-5.6 Sol model, produced 166 exploitable flaws for approximately $514,000. The new campaign finds more than five times as many, while the core had benefited from three months of additional strengthening in the meantime.
OpenAI also compares this cost to bounties paid in hacking competitions, where a breach of this type can bring in between $20,000 and $70,000. At this price, the 948 flaws would be worth between $18.9 and $66.3 million, or sixteen to fifty-five times the cost of the campaign. This calculation remains theoretical, but it shows that finding flaws becomes much cheaper.
The researchers finally examined a sample of 166 attacks and identified at least ten previously undocumented exploitation techniques, according to outside kernel experts.
Where are the fixes?
For each flaw, the channel proposed a fix. According to the reported figures, ten days after the analysis, 61 flaws were corrected in the official kernel version, 43 had a fix in the works and 299 were reported and discussed publicly. OpenAI says it has followed the recommendations of the Linux kernel community for transmitting its reports, as part of its Patch the Planet program.
The number of 948 therefore refers to flaws validated with a proposed fix, and not 948 fixes already integrated. Most still need to be examined by volunteer or company-employed maintainers, whose workload increases with this type of serial discovery. OpenAI has not published technical details of the attacks. This restraint, usual in IT security, gives time for patches to be released before attackers can take inspiration from the methods used.
A double-edged sword
This capability benefits defenders: known and corrected flaws can no longer be used by attackers. But the same tool, in the wrong hands, would drastically reduce the time between publishing a kernel modification and developing a working attack. Hence the importance, underlined by observers, of human proofreading and control of patches by maintainers.
It is also for this reason that the most powerful models in cybersecurity are primarily reserved for defenders, like the Gemini 4 Carbon, open primarily to cyberdefense specialists. The discovery of flaws by AI also extends to other widespread software, as shown by the critical PHP flaws found using AI in October 2026.
What users and administrators should do
For individuals using Linux as well as for companies operating servers, the instructions are simple: quickly apply updates. The fixes will gradually arrive in the kernel versions, then in the distributions.
- Enable automatic security updates on workstations and servers when possible.
- Reboot after a kernel update: the new kernel is only active after a reboot, except hotfix tools.
- Limit accounts and programs which have access to each machine, since these flaws require first access.
- Monitor security bulletins of its distribution, which report kernel fixes.
- For devices that you cannot update yourself, such as certain connected objects or old phones, check the manufacturer’s update policy.
Towards transformed IT security
The OpenAI campaign confirms a fundamental trend: AI makes the search for vulnerabilities massive, fast and inexpensive. For free software like Linux, which relies on communities of maintainers, the challenge now is to absorb this flood of reports and fixes without sacrificing the quality of verifications. For users, cybersecurity will require regular updates more than ever, while attackers also have these tools.